Categories
Cyber Security

Remote Access Security for UK Businesses

A director approving a supplier invoice from home, a colleague checking Microsoft 365 on a mobile, or an engineer connecting to a server after hours: each task can be necessary for the business to keep moving. It also creates a route into valuable systems and data. Effective remote access security lets people work where they need to, without leaving leaders to worry that one lost password or unmanaged laptop could become a serious incident.

For UK small and medium-sized businesses, the challenge is rarely a lack of security products. It is making sure the right protections work together, are properly managed and do not make everyday work unnecessarily difficult. The aim is practical control: knowing who can access what, from which device, and what happens if something goes wrong.

Where remote access security breaks down

Remote working is not limited to employees permanently based at home. It includes travelling staff, temporary workers, external IT support, directors using personal mobiles and team members accessing cloud applications outside normal hours. Every connection may be legitimate, but it should not automatically be trusted.

Weak or reused credentials

Stolen credentials remain one of the simplest ways for criminals to enter a business. A convincing phishing email can capture a Microsoft 365 password in minutes, particularly if a member of staff is under pressure or believes they are responding to a genuine request.

If that password is reused elsewhere, exposed in an old breach, or not protected by multi-factor authentication, an attacker may be able to read email, reset other passwords, request payments or move through connected systems. Business email compromise often begins this way, and the financial and reputational damage can be significant.

Devices outside the office

An office network is generally easier to control. Devices used remotely may be on home broadband, public Wi-Fi or mobile data, and may not receive updates as reliably as company equipment. A laptop without current security updates, endpoint protection or disk encryption can expose business information if it is compromised, lost or stolen.

Personal devices deserve particular care. They can be suitable for limited access in some organisations, but only where clear rules and technical controls are in place. Allowing unrestricted access from any device is convenient until it becomes impossible to confirm where sensitive data has been saved.

Too much access for too long

Remote access should reflect a person’s role, not simply their employment status. A finance administrator does not need the same access as a director, and a third-party supplier should not retain an active account after a project has finished.

Excessive permissions increase the impact of a compromised account. They can also create compliance concerns for professional services firms and regulated organisations handling client, financial or personal data. Good access control is about reducing unnecessary exposure, not making people ask permission for every routine task.

The controls that make remote access safer

There is no single setting that delivers effective remote access security. Protection comes from layers that support one another, with a clear process behind them. The following measures are a sensible foundation for most businesses.

  • Multi-factor authentication adds a second check when someone signs in. It is one of the strongest defences against password theft, especially for Microsoft 365, remote desktop tools, finance systems and administrator accounts.
  • Managed devices ensure laptops and mobiles have current updates, endpoint protection, encryption and the ability to be locked or wiped if they are lost. This gives the business more control without relying on staff to remember every technical task.
  • Conditional access policies can require a compliant device, a trusted location or extra verification before allowing access to sensitive applications. They help stop risky sign-ins without blocking normal work unnecessarily.
  • Least-privilege access limits users to the files, systems and administration rights they genuinely need. Privileged accounts should be separately controlled and used only for administrative work.
  • Monitoring, backup and recovery provide a safety net. Sign-in alerts can highlight unusual activity, while protected backups help the business recover if ransomware, accidental deletion or account compromise affects cloud or on-premises data.

The detail depends on how your organisation operates. A logistics business with staff using shared devices and working around the clock will have different requirements from a legal practice where confidential documents are accessed by a smaller group. The principle remains the same: access should be intentional, visible and recoverable.

Remote access security is also a people issue

Technical controls reduce opportunity, but people still make decisions at the point of attack. Criminals know this. They create fake Microsoft alerts, imitate senior colleagues and use urgent payment requests because these tactics exploit normal working pressures.

Short, relevant training is more useful than a once-a-year presentation filled with jargon. Staff should know how to recognise suspicious sign-in prompts, report a phishing email, use a password manager and respond if a device is lost. They should also feel able to pause and ask for help without embarrassment.

This matters most for colleagues with access to finance, client records, HR information or administrative systems. A tailored phishing awareness programme can focus on the situations they actually face, rather than generic examples that are easy to dismiss. The result is a more alert team and fewer avoidable incidents.

Make protection fit the way your business works

Security controls fail when they are introduced without considering operational reality. If multi-factor authentication is difficult for a warehouse supervisor moving between shifts, they may look for workarounds. If a director cannot access a critical document while travelling, they may send it to a personal email account. Neither response is careless by design; both are signs that the process needs improving.

Start by mapping the services your people access remotely, the information held in each one and the roles that need access. Include less obvious systems such as remote support software, online accounting, document-sharing platforms, printers, network equipment and backup consoles. These are often overlooked, yet they can offer a direct route into the business.

Then agree sensible rules. For example, company-managed laptops may be required for access to sensitive client files, while mobile access is allowed only through approved applications. External support accounts may be time-limited, and finance approvals may need an additional verification step. Clear rules make it easier for staff to do the right thing and for managers to spot exceptions.

Who should manage remote access?

Some technically capable businesses prefer to manage access policies, devices and alerts internally. This can work well where there is enough expertise and time to review alerts, maintain documentation and respond quickly when a staff member leaves or a device is missing.

For many smaller organisations, however, security administration competes with customer service, operations and growth. In that case, managed support can remove a considerable burden. A specialist team can help configure security policies, monitor risks, manage user changes and provide a real person to call when something does not look right.

There is also a middle ground. A business may manage its everyday IT while bringing in professional support for a security review, Microsoft 365 hardening project, incident response planning or backup test. What matters is clear accountability. Someone must own the routine checks, access reviews and response process rather than assuming they are being handled.

Test the response before it is needed

Remote access security is not complete because the controls have been switched on. Test what happens when a colleague reports a suspicious sign-in, loses a laptop or leaves the business unexpectedly. Can access be removed promptly? Can the device be secured? Does the team know who decides whether clients, insurers or regulators need to be informed?

Regular access reviews are equally valuable. Remove dormant accounts, check administrator rights, confirm that multi-factor authentication remains enforced and review whether old suppliers still have a reason to connect. These tasks are not glamorous, but they close the gaps that attackers look for.

The best arrangement is one that gives your people the freedom to work productively while keeping the business in control. Put clear protections in place, make them straightforward to use and ensure expert help is available when the pressure is on. That is one less thing to worry about while you focus on running the business.
Categories
Cyber Security

Can Ransomware Spread Across Your Business?

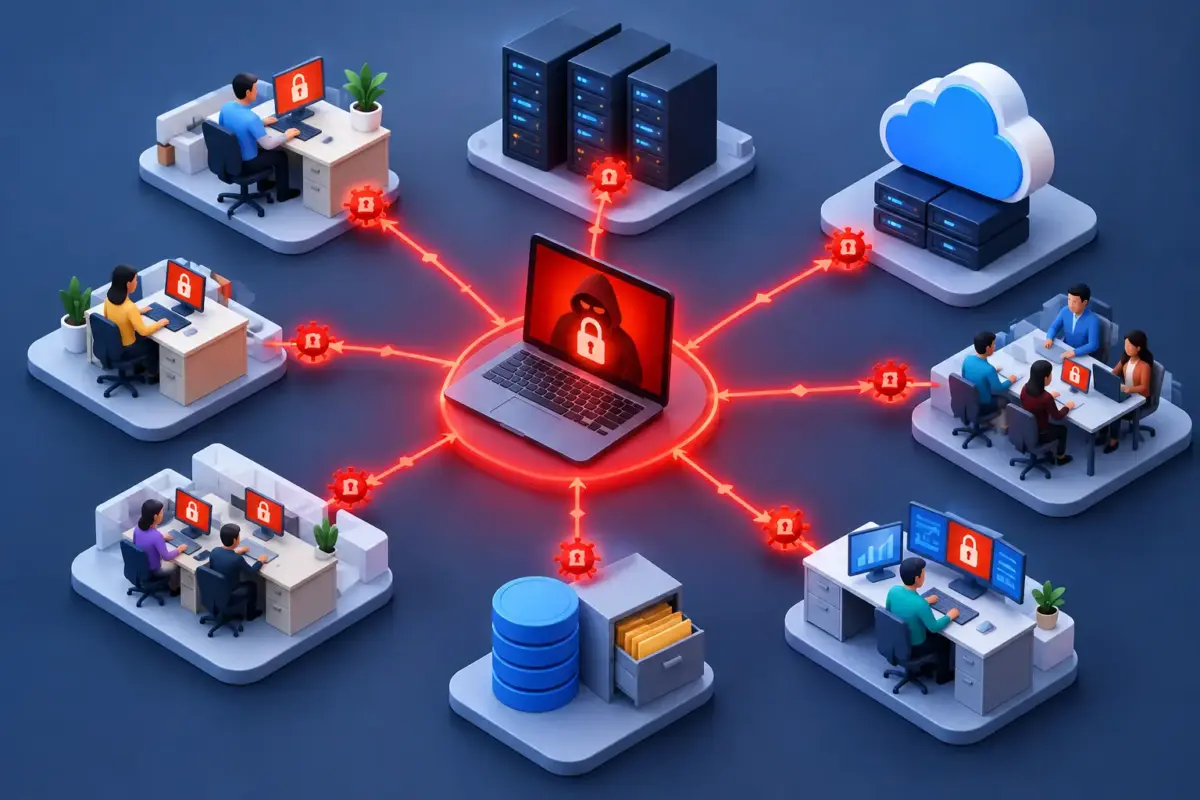
A single encrypted laptop is disruptive. A whole business unable to access client files, dispatch systems, accounts data or Microsoft 365 is a continuity incident. So, can ransomware spread? Yes. Depending on the strain and the access an attacker gains, ransomware can move from one device or account to shared systems across your organisation.

The good news is that spread is not inevitable. The right mix of technical controls, sensible access rules, staff awareness and tested backups can turn a potentially business-wide outage into a contained incident. For a small or medium-sized business, that is the difference between a difficult day and a damaging interruption to operations, revenue and reputation.

Can ransomware spread from one computer to another?

Some ransomware is designed to spread automatically. It may look for vulnerable devices, open network shares or weakly protected remote access services, then copy itself to other machines. This is often described as worm-like behaviour. Once inside, it can move quickly, particularly in organisations where devices are all connected to the same network with broad permissions.

Other attacks spread because the criminal has access, not because the ransomware itself is self-propagating. An attacker may steal an employee’s password through a phishing email, log into a Microsoft 365 account, access a file server or use remote management tools, and deploy ransomware across several endpoints. In these cases, the initial infection is only the start of the attack.

That distinction matters. A business can have antivirus on every PC and still be exposed if a compromised administrator account can reach every server, shared folder and backup location. Ransomware prevention is therefore about limiting both malicious software and the paths an attacker can use once they get in.

How ransomware moves through a business

Ransomware does not need a dramatic Hollywood-style breach to cause widespread damage. It often begins with a familiar business activity: an invoice attachment, a fake Microsoft 365 sign-in page, an unpatched laptop, or a remote desktop service exposed to the internet.

Shared drives and file servers

An infected device can encrypt files on network drives that the signed-in user can access. If a member of staff has permission to amend a department-wide folder, ransomware may encrypt the files there too. Shared drives are particularly vulnerable where permissions have grown over time and many users have more access than their roles require.

File servers may also be targeted directly. If an attacker obtains a privileged account, they can disable security tools and launch encryption across large volumes of data. The speed of this activity can leave little time to react without monitoring and an agreed incident response process.

Stolen credentials and administrator access

Criminals value credentials because a legitimate login is less likely to raise immediate suspicion. They may reuse a password leaked in an unrelated breach, trick a user into approving a multi-factor authentication request, or take over an email account through phishing.

Once inside, they look for accounts with higher permissions. An administrator account that is used for day-to-day email and browsing creates an unnecessary opportunity. If it is compromised, ransomware can be pushed to many devices at once using tools that IT teams themselves rely on for management.

Email, cloud storage and Microsoft 365

Email is usually a delivery route rather than a way for ransomware to infect every mailbox automatically. A convincing message can be sent from a compromised internal account, making colleagues more likely to trust it. Each person who opens the attachment or follows the link creates another possible foothold.

Cloud services change the picture rather than removing the risk. A ransomware infection on a synchronised computer can encrypt local copies of files, after which the encrypted versions may synchronise to SharePoint, OneDrive or Teams. Account compromise can also allow attackers to delete files, create forwarding rules, steal information and disrupt access without encrypting a single device.

Remote workers, suppliers and unmanaged devices

Remote working is not inherently unsafe, but unmanaged home devices and informal file-sharing habits can weaken controls. A personal computer used to access company data may not have the same updates, endpoint protection or monitoring as a managed laptop.

Suppliers can create another route where they have remote access, shared credentials or access to sensitive systems. The practical question is not whether every third party is a risk. It is whether each connection has a clear purpose, appropriate permissions and a secure method of access.

What makes ransomware spread faster?

Flat networks, shared local administrator passwords and overly broad file permissions make it easier for an attacker to move around. So do delayed software updates, unsupported systems and remote access services without multi-factor authentication. These weaknesses are common because businesses need staff to work efficiently, not because anyone has deliberately ignored security.

There are trade-offs. Restricting access too aggressively can slow down a busy team, especially in professional services, logistics or other operationally demanding environments. The aim is not to lock every system down until work becomes difficult. It is to give people the access they need, while preventing a compromised account from reaching everything else.

Attackers also try to slow your response. They may disable security software, delete backup copies they can reach, or remain unnoticed for days while they identify valuable data. Many modern ransomware groups steal information before encrypting it, then threaten to publish it. Restoring files alone may not resolve the legal, commercial and client-confidence consequences.

Controls that help contain an attack

No single product stops every ransomware attack. Effective protection layers controls so that a mistake by one person or failure of one system does not become a business-wide event.

Start with endpoint protection that can detect suspicious behaviour, isolate an affected device and alert the right people quickly. The ability to isolate a laptop from the network without waiting for someone to find it can prevent further spread. Keep operating systems, browsers, applications and network equipment patched, with particular attention to systems exposed to the internet.

Use multi-factor authentication for email, cloud applications, remote access and administrator accounts. Pair it with credential management and a clear process for removing access when staff or suppliers leave. Administrative accounts should be separate from everyday user accounts, and privileged access should be granted only where it is genuinely required.

Review file permissions and segment your network so that a compromise in one area does not automatically reach every server or device. For many SMEs, this is best approached in stages: identify the most critical systems first, reduce unnecessary access, then improve separation as systems are renewed or projects are planned.

Email filtering and browsing protection can reduce the number of malicious links and attachments that reach staff. They are valuable safeguards, but not a reason to assume every dangerous message will be caught. Regular ransomware and phishing awareness training helps people spot unusual requests, report them early and avoid turning a suspicious email into an incident.

Finally, maintain backups that are separate from your main environment and test them. A backup that has never been restored is an assumption, not a recovery plan. Test whether you can restore the data that matters most, how long recovery will take and who has authority to make decisions if systems are unavailable.

What to do if you suspect ransomware is spreading

Speed matters, but so does avoiding a rushed response that destroys useful evidence. Disconnect the affected device from Wi-Fi and wired networks if you can do so safely. Do not reconnect it simply to check whether the problem has cleared. Tell your IT provider or internal IT lead immediately, and ask staff not to open unexpected emails or attachments while the situation is assessed.

Do not delete files, wipe devices or pay a ransom before qualified advice is available. These actions can complicate investigation and recovery. Your response should establish what has been affected, whether accounts are compromised, whether data has been taken and whether backups remain safe. If personal or confidential information may be involved, you may also need to consider contractual, regulatory and insurance obligations.

A documented incident plan makes these decisions less stressful. It should include current contact details, the location of recovery information, a method for communicating if email is unavailable, and clear responsibilities for technical, operational and client-facing decisions.

Ransomware spreads where access is too broad, warning signs are missed and recovery is untested. Reducing those gaps is one less thing to worry about when your team has clients to serve and a business to run.

Categories
Cyber Security

How to Report Suspicious Emails at Work Safely

A convincing email can arrive at exactly the wrong moment: just before a payment run, during a busy client deadline, or while a colleague is on holiday. Knowing how to report suspicious emails gives your IT team the chance to stop a wider problem before a rushed click becomes stolen credentials, a fraudulent payment or downtime for the business.

The aim is not to make every member of staff a cybersecurity expert. It is to give people a simple, repeatable response when something does not feel right: do not interact with it, report it through the right route, and let the right people investigate.

Why reporting a suspicious email matters

Many harmful emails do not look obviously malicious. They may appear to come from Microsoft 365, a supplier, a senior colleague or a delivery company. Some use a familiar logo, a real person’s name or a message that seems relevant to your role. Business email compromise attacks can be particularly persuasive because criminals may first gain access to a genuine mailbox, then use it to request a change of bank details or a sensitive document.

Deleting an email protects one inbox, but reporting it can protect everyone. Your IT provider or internal team can check whether the message reached other colleagues, block the sender or website, remove matching emails and look for signs that an account has already been affected. That is a small action with a potentially significant operational benefit.

Not every unwanted email is an urgent incident. A newsletter you do not remember signing up for may simply need unsubscribing from or filtering. A suspicious email is different: it tries to make you disclose information, open a file, scan a QR code, visit a website, approve a sign-in, make a payment or bypass normal process.

How to report suspicious emails without creating more risk

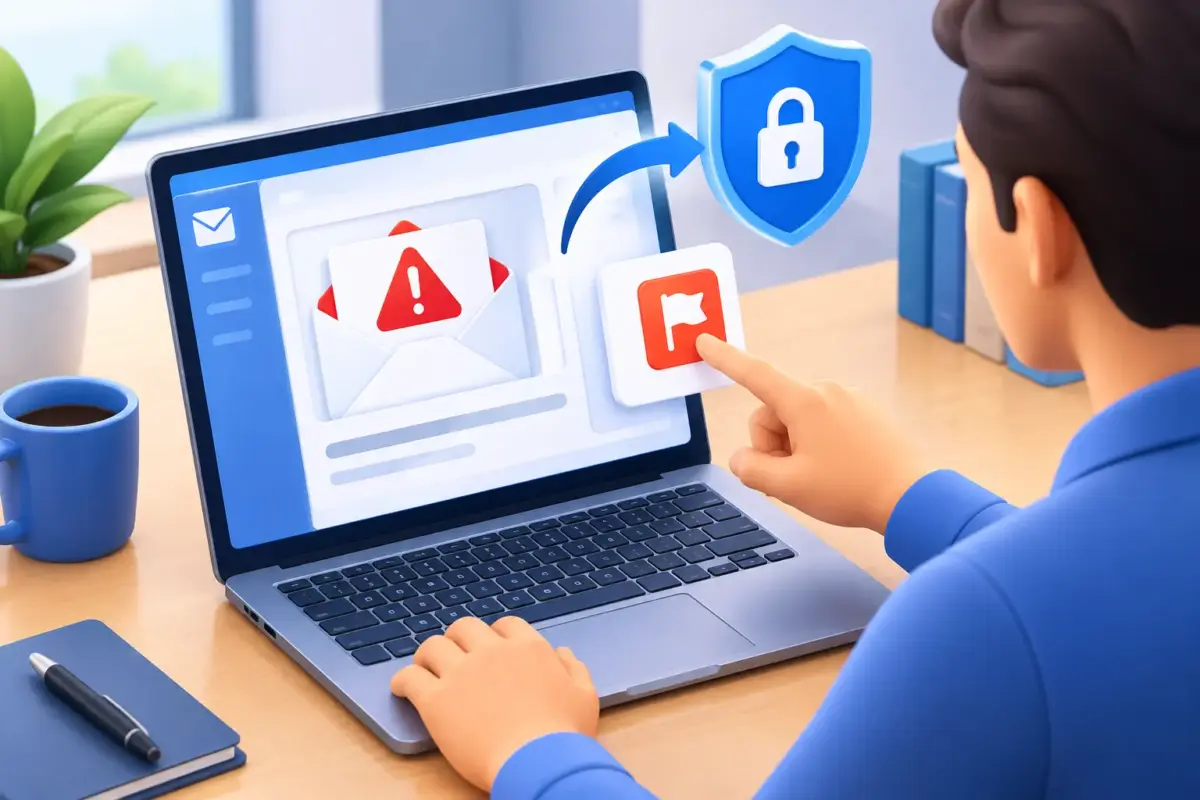
Use your organisation’s reporting process first. For many Microsoft 365 users, this will be a built-in Report Message or Report Phishing button in Outlook. If your business uses a security awareness platform or helpdesk portal, it may have its own reporting option. These methods allow the security team to receive the original message and its technical details.

If you are not sure which process applies, contact your IT support team by a trusted method, such as the usual helpdesk number, support portal or Teams channel. Do not reply to the suspicious email to ask whether it is genuine, and do not use contact details contained in it.

Follow these four steps:

  1. Pause before clicking. Do not open attachments, follow links, scan QR codes or enter your password. Avoid replying, even to challenge the sender.
  2. Report the message using the approved tool. Use the phishing-reporting button or your helpdesk process. This is preferable to simply forwarding it.
  3. Leave it in place until advised otherwise. Your IT team may need to review the message headers, recipient details and attachments. If the reporting tool removes it automatically, that is fine.
  4. Tell IT if you interacted with it. Be clear about what happened, including whether you opened a link, entered a password, downloaded a file or approved a multi-factor authentication prompt.

Forwarding can be useful when your IT team specifically asks for it, but it has drawbacks. A standard forward may lose valuable technical information and can expose another person to a harmful link or attachment. Where required, send the email as an attachment rather than copying its contents, and follow the instructions your support provider gives you.

What information should you include?

A short report is enough to start with. Mention why the email caught your attention, such as an unusual sender address, an unexpected invoice, poor wording, an urgent request from a director, or a link that did not match the claimed website. Say whether anybody else received it, if you know.

Screenshots can help, especially if the message was viewed on a mobile device. However, the original email is more useful than a screenshot because it contains evidence that can help identify the source and scope of the attack. Your team may also ask for the time received and the device used.

If you clicked a link or opened an attachment

Report it immediately. Speed matters more than embarrassment. Cybercriminals rely on people feeling they should quietly fix a mistake themselves. In practice, prompt reporting gives your IT team more options to contain the issue.

If you entered a password into a website, use a known, trusted route to change that password straight away. Do not return to the page from the email. If you reuse that password elsewhere, those accounts may also need attention, particularly email, finance and cloud services. Your support team can advise on the right order of action and check whether there were unfamiliar sign-ins or mailbox rule changes.

If you downloaded or opened a file, disconnecting from the network may be appropriate, but this depends on your organisation’s incident procedure and the device involved. Call IT rather than spending time investigating it yourself. Do not delete files, clear browser history or restart the device unless instructed, as that can remove evidence needed to understand what happened.

If the email asked for payment details or a bank-account change, pause the transaction and verify the request independently. Call the supplier or colleague using a number already held in your records, not one in the email. This simple control remains one of the strongest defences against invoice fraud.

Recognising messages that deserve a report

No single warning sign proves an email is malicious. Legitimate messages can contain typos, and criminals can copy a genuine signature perfectly. Look for a combination of signals and trust the processes your business already uses.

Common warning signs include a slight change in a familiar domain name, an unexpected document-sharing request, urgency that discourages checking, payment instructions outside the normal workflow, or a request for login details. Be cautious with emails claiming that a mailbox will be closed, a password has expired or a parcel cannot be delivered. These themes are designed to create pressure.

It also depends on context. An invoice from a regular supplier may be expected, but a new bank account on that invoice should still be verified through your established finance process. A message from a director may look legitimate, but a request to buy gift cards, share payroll data or approve a sign-in code should be treated as unusual unless verified independently.

Make reporting easy for every colleague

A good reporting process should work for a receptionist handling deliveries, a finance manager approving invoices and a remote employee checking messages from a phone. If people must remember a complicated chain of escalation, valuable minutes are lost and fewer emails are reported.

Set a clear internal rule: when in doubt, report it. Make sure staff know where the reporting button is, how to contact IT outside normal hours and what will happen after they raise a concern. Regular phishing awareness training helps, but it is most effective when paired with practical protections such as email filtering, multi-factor authentication, endpoint protection and monitored Microsoft 365 security.

Leaders also set the tone. Thank staff for reporting concerns, including false alarms. A culture that punishes people for asking questions encourages silence, while a culture that values early reporting reduces the chance of a small issue becoming a business interruption.

When an external report may be appropriate

Your IT team should normally coordinate the initial response, particularly if business systems, customer data or payment information may be involved. They can preserve evidence, assess notification obligations and decide whether the message should be reported to the National Cyber Security Centre’s Suspicious Email Reporting Service or another relevant authority.

For UK businesses, this is especially useful where the email impersonates a well-known organisation or forms part of a broader phishing campaign. If money has been sent or a payment is being diverted, contact your bank immediately as well as escalating internally. The right response may involve finance, legal and data protection contacts, depending on the information involved.

A suspicious email does not have to become a security incident. When people can report it quickly, without uncertainty or blame, it becomes one less thing to worry about and one more threat your business has handled properly.

Categories
Cyber Security

Best Email Security Gateways for UK Businesses

A convincing-looking invoice, a spoofed message from a director, or a shared Microsoft 365 file that is not what it appears to be can all arrive through the same route: email. The best email security gateways do more than filter obvious spam. They help UK businesses stop phishing, business email compromise and malicious attachments before staff have to make a difficult judgement call.

For a growing business, the right choice is rarely the platform with the longest feature list. It is the one that fits your existing Microsoft 365 environment, protects the threats you actually face and is managed well enough that warnings, quarantined messages and policy changes do not become another job for a busy operations team.

What an email security gateway should do

An email security gateway sits between the internet and your users’ inboxes. It inspects incoming and, in many cases, outgoing messages for signs of risk. That can include known malware, suspicious links, impersonation attempts, unusual sender behaviour and sensitive information leaving the business.

Modern attacks make this harder than it sounds. Criminals no longer rely only on poorly written spam. They use compromised legitimate accounts, copied branding, real supplier names and messages timed around payroll, invoice runs or annual leave. Some messages contain no attachment or malicious link at all. Their aim is simply to persuade someone to change bank details, buy gift cards or share a password.

A useful gateway therefore combines several layers of protection. It should check sender authenticity through controls such as SPF, DKIM and DMARC; scan attachments and web links; identify impersonation; and provide clear quarantine and reporting tools. It should also support encryption, data loss prevention or archiving where these are relevant to your business.

No gateway can guarantee that every unwanted message will be stopped. The practical objective is to reduce the number of dangerous messages reaching staff, make the remaining risks easier to recognise, and give your organisation a fast way to investigate and respond.

The best email security gateways are not identical

There is no single best product for every UK small or medium-sized business. The right platform depends on the size of your team, the sensitivity of your information, whether you run Microsoft 365, and who will manage the system day to day.

The products below are commonly considered by organisations looking for stronger email protection. Their strengths overlap, but their operating models and costs can differ significantly.

Microsoft Defender for Office 365

For businesses already using Microsoft 365, Defender for Office 365 is often the most natural starting point. It is integrated with Exchange Online and Microsoft’s wider security tools, which can make deployment, alerting and investigation more straightforward. Features can include anti-phishing policies, Safe Links, Safe Attachments, impersonation protection and post-delivery investigation capabilities, depending on the licence level.

Its main advantage is integration. Security teams or managed providers can see email events alongside identity, endpoint and cloud activity, which matters when a phishing email leads to a compromised account or suspicious login.

The trade-off is that the platform needs careful configuration and ongoing attention. Default settings are not the same as a security strategy. Smaller businesses may also find Microsoft licensing difficult to interpret, particularly where advanced capabilities sit in higher-tier plans. It is a strong option when it is properly tuned and actively monitored, rather than simply switched on.

Mimecast

Mimecast is widely used by businesses that want a dedicated email security platform with a broad set of capabilities. It is known for email filtering, continuity services, impersonation protection, archiving and policy controls. For organisations with a larger email estate, compliance requirements or a need for more detailed email governance, this breadth can be attractive.

Email continuity can be particularly valuable where an outage would prevent teams from communicating with customers, suppliers or colleagues. If your organisation handles sensitive client records or relies on email to keep operations moving, that additional resilience may justify the investment.

The consideration is complexity. A feature-rich platform needs clear policies and knowledgeable administration. Without that, staff can face unnecessary quarantine messages or legitimate communications may be held back. Businesses should establish who owns day-to-day management before committing.

Proofpoint

Proofpoint has a strong reputation for advanced threat protection and for analysing the human side of email risk. Its tools are often well suited to organisations that receive significant volumes of targeted phishing, work with valuable financial data, or need detailed visibility into potentially risky communications.

This can make it a sensible consideration for professional services firms, finance teams and regulated organisations where a successful account takeover could have serious consequences. Its wider security portfolio can also support training and user-focused risk programmes.

For a smaller organisation, however, the question is whether the service level and administration requirements are proportionate to the risk. A sophisticated platform is only valuable if someone has time to interpret alerts, refine policies and act on the findings. Managed support can make the difference between a capable product and a practical service.

Barracuda Email Protection

Barracuda offers email protection with capabilities around phishing, malware, impersonation and account takeover. It can appeal to businesses that want a focused security layer for Microsoft 365 or Google Workspace without building a large in-house security operation.

Its appeal is often in combining core email defences with policy control and backup or continuity options, depending on the package selected. This can suit an organisation looking to address several related email risks through a single supplier.

As with every gateway, assess how it will handle your normal business communications. Ask to test supplier invoices, password-protected files, scanned documents and messages from overseas contacts where relevant. A system that blocks threats but repeatedly interrupts legitimate work will lose staff confidence quickly.

How to choose an email security gateway without overbuying

Start with the incidents that would cause the greatest disruption. A logistics business may be especially exposed to fraudulent delivery instructions and supplier invoices. A legal or accountancy practice may be more concerned about client confidentiality, payment diversion and retention requirements. A business with remote workers may need stronger account takeover protection and clearer ways to report suspicious messages.

Then consider these practical questions:

  • Does the gateway work well with your Microsoft 365 licence and email setup?
  • Can it detect impersonation of directors, finance staff, suppliers and trusted domains?
  • Are attachments and links checked before and after delivery?
  • Can administrators trace a message quickly and remove a harmful email from multiple inboxes?
  • Will users receive understandable quarantine notices without being expected to make technical security decisions?
  • Does the provider offer real support when an urgent message is suspected to be fraudulent?

The final point is easily overlooked. During a suspected payment fraud incident, a generic support queue is not much reassurance. Your team needs to know who can check the message, help contain any exposure and advise on the next steps.

Gateway protection still needs people and process

Email security is not solved at the gateway. Criminals can use personal email accounts, compromised supplier accounts, telephone calls and collaboration platforms to continue a conversation. They also adapt quickly when a particular tactic stops working.

That is why technical controls should sit alongside short, relevant staff awareness training. Finance teams need a firm process for verifying bank detail changes. Directors and managers need to understand why their names are frequently impersonated. Everyone should know how to report a suspicious message without worrying that they are wasting IT’s time.

It also helps to review the basics around identity. Multi-factor authentication, strong password management, prompt removal of departing users and regular checks for suspicious mailbox rules all reduce the damage that follows a successful phishing attempt. Reliable backups provide another layer of protection if ransomware or account compromise affects business data.

Managed protection can remove the day-to-day burden

Many SMEs do not need to employ a full-time security specialist to improve email protection. They do need clear accountability for configuration, monitoring and support. A managed service can provide that oversight while leaving leaders free to focus on clients, staff and day-to-day operations.

MSnet helps organisations combine email protection with Microsoft 365 security, endpoint controls and practical phishing awareness. The aim is not to add another dashboard for your team to watch. It is to put sensible safeguards in place, explain what matters in plain English and make help available when something does not look right.

Choosing from the best email security gateways is ultimately about confidence, not just filtering scores. Select a solution your business can run well, test it against real communication patterns, and make sure your people have a clear route to human support when a questionable email lands in their inbox.

Categories
Cyber Security

When IT Outsourcing Makes Good Business Sense

A director receives an email supposedly from a major supplier, asking for revised bank details. At the same time, a member of staff cannot access Microsoft 365, and the person who normally “looks after IT” is on holiday. These are not separate inconveniences. They are the moments when IT outsourcing either proves its value or exposes a gap in how a business is supported.

For many UK small and medium-sized businesses, technology is now tied directly to revenue, customer confidence and compliance. Systems need to work, data needs to be protected and people need a real person to call when something goes wrong. The question is not whether your organisation needs IT expertise. It is whether employing, managing and retaining all of that expertise in-house is the best use of your time and budget.

What IT outsourcing should mean for your business

IT outsourcing is the use of an external technology partner to take responsibility for agreed parts of your IT environment. That could range from day-to-day helpdesk support and device management to cybersecurity monitoring, cloud backup, Microsoft 365 protection or a one-off infrastructure project.

It should not mean handing over the keys and hoping for the best. A good provider works as an extension of your business: understanding how your team works, explaining risks in plain English and taking clear ownership of the areas it manages. You remain accountable for business decisions, but you are no longer expected to be the expert in every technical detail.

This distinction matters. Buying software is not the same as having a plan for configuring it, monitoring it, keeping it up to date and helping staff use it safely. Most successful outsourced arrangements combine the right technology with responsive support, sensible processes and guidance for the people who use the systems every day.

When outsourced IT is the right choice

Outsourcing is often a practical fit when a business has become too dependent on one technically capable employee, an informal IT contact or a collection of suppliers with unclear responsibilities. It can also make sense when growth, remote working or client requirements have made the existing approach difficult to manage.

For example, a professional services firm may need confidence that confidential client information is protected, backed up and recoverable. A logistics business may need systems available outside standard office hours, because operational delays have an immediate commercial effect. A growing owner-managed company may simply need its leadership team to stop spending Friday afternoons dealing with password resets, new laptops and suspicious emails.

The strongest case for outsourcing is rarely a single crisis. It is the accumulated pressure of small issues, hidden risks and uncertainty about who is responsible when something fails.

Signs that your current arrangement is under strain

There are several common warning signs. Staff wait too long for help, routine changes happen inconsistently, and no one can clearly explain whether backups have been tested. Cybersecurity depends largely on employees spotting phishing emails, yet they have received little practical training. Former staff accounts remain active, devices are not consistently updated, or important systems are supported by a person who is difficult to reach.

None of these problems necessarily means your team has been careless. Smaller businesses frequently grow faster than their IT processes. What worked when ten people shared one office can become risky when fifty people work across home, client and warehouse locations.

The business benefits are broader than technical support

A capable outsourced provider should reduce interruptions, but that is only one part of the value. The larger benefit is predictability. Leaders can see what is being managed, what the risks are and what the ongoing costs look like.

Cybersecurity is a clear example. Endpoint protection, email filtering, secure browsing, credential management and monitoring for exposed information can all reduce the chance of an attack succeeding. Yet technical controls alone cannot prevent every incident. Staff also need to understand how phishing, business email compromise and password theft appear in real working situations.

This is where practical training matters. A short, relevant programme that helps people pause before approving a payment request or entering credentials into a lookalike website can prevent a costly incident. The aim is not to make every employee a security specialist. It is to give them the confidence to recognise when something does not look right and know what to do next.

Reliable backup and recovery provide another important layer of reassurance. Cloud-based working has led many businesses to assume their Microsoft 365 data is automatically protected in every circumstance. Retention, recovery and protection against accidental deletion or malicious activity need to be considered separately. A backup is valuable only if it is suitable for the data you hold and can be restored when you need it.

Outsourcing can also support better budget control. Rather than reacting to unexpected failures, licences, ageing hardware and security gaps one at a time, a business can agree a managed service with defined responsibilities and regular reviews. The exact commercial model varies, but clear scope reduces unpleasant surprises.

What should stay within your organisation

Outsourcing does not remove the need for internal ownership. Your leadership team should still set priorities, approve spending and decide what level of risk is acceptable. Sensitive business decisions, such as who should have access to financial systems or which data must be retained, should remain led by people who understand the organisation.

The right partner brings technical judgement and challenges assumptions where necessary. The business provides context: its clients, operational pressures, contractual commitments and plans for growth. Good decisions come from both sides.

It is also worth recognising that not every organisation needs the same level of managed support. A technically confident internal team may prefer self-managed tools with expert help available for projects or complex issues. A business with no dedicated IT resource may benefit more from a fully managed service and an accessible helpdesk. The appropriate model depends on internal capability, risk exposure and how disruptive downtime would be.

Choosing an IT outsourcing partner carefully

Price matters, but it should not be the only comparison point. A low monthly figure can look attractive until an urgent issue falls outside scope, a cyber incident reveals a missing service, or staff are forced through slow, impersonal support channels at a critical moment.

Ask prospective providers how support actually works. Will your staff speak to experienced people who understand the account, or will every issue start from scratch? What response expectations apply? How are urgent problems escalated? What reporting will leadership receive, and how often will risks be reviewed?

Cybersecurity questions should be equally specific. Find out how devices, email, identities and backups are protected. Ask whether staff awareness training is included and whether recovery arrangements are tested rather than simply assumed. If your business operates in a regulated sector or handles sensitive customer information, discuss your obligations openly. A provider should help you make sensible decisions, not hide behind technical language.

You should also seek clarity about responsibilities. The agreement should explain what the provider manages, what your business must do, how changes are requested and what happens if an incident occurs. Clear boundaries are reassuring because they remove the uncertainty that causes delays during a problem.

A sensible way to make the change

Moving to outsourced support need not mean replacing everything at once. Begin with an honest review of your current environment: users, devices, software, access rights, backups, recurring issues and known risks. This gives both parties a practical starting point and helps identify the most urgent actions.

Many businesses benefit from tackling the basics first. Multi-factor authentication, secure account management, patching, endpoint protection, email security and verified backups address a large share of everyday risk. From there, a longer-term plan can cover hardware replacement, cloud improvements, staff training and business continuity.

The transition should be planned around the organisation, not around the provider’s convenience. Your team needs to know who to contact, what will change and when. Communication is particularly important if new security measures affect how people sign in, share files or work remotely. A little preparation reduces frustration and encourages adoption.

MSnet’s approach is built around this practical balance: technical safeguards, human support and services that match the level of help a business genuinely needs. For leadership teams, that means less time interpreting alerts or chasing suppliers, and more confidence that technology is being looked after.

The best outsourced IT relationship is not one you notice every day. It is the quiet confidence that when a suspicious email arrives, a laptop fails or a client asks how their data is protected, your business has a clear answer and real people ready to help.

Categories
Cyber Security

Account Takeover Detection for UK Businesses

A stolen password rarely looks dramatic at first. A criminal may sign into a Microsoft 365 account, read messages quietly, set up an inbox rule and wait for the right invoice or payment request. Effective account takeover detection gives your business a chance to spot that activity before a compromised account becomes fraud, data loss or a wider ransomware incident.

For UK small and medium-sized businesses, this matters because email, cloud applications and remote access are central to daily work. One account can hold customer information, commercial documents, payment details and the authority to request urgent action from colleagues. Detecting suspicious access early is one less thing to worry about for leaders responsible for continuity, compliance and cash flow.

What an account takeover looks like in practice

An account takeover occurs when someone gains unauthorised access to a legitimate user account. They do not necessarily need to break into your network. More often, they use a password collected through phishing, bought from a criminal marketplace after a third-party breach, or reused from another service.

Attackers are also becoming more adept at getting around basic security habits. A convincing fake Microsoft 365 sign-in page can capture credentials and a one-time code. Repeated multi-factor authentication prompts can pressure a busy employee into approving one by mistake. In more targeted attacks, criminals steal browser session tokens, allowing them to impersonate a logged-in user without entering a password again.

The first signs can be subtle. A user may receive a notification about a sign-in they do not recognise, or a colleague may notice an unusual request from a familiar email address. In other cases, there is no warning until a supplier’s bank details are changed or sensitive files have been copied.

How account takeover detection works

Account takeover detection is not one product or alert. It is the process of comparing normal user activity with activity that does not fit, then giving the right people enough information to investigate and act quickly.

A good approach combines identity controls, endpoint protection, email security and informed staff. Each layer catches something different. Sign-in monitoring may flag an impossible journey between locations or access from an unfamiliar device. Email protection may identify suspicious forwarding rules. Endpoint tools can detect malware or a compromised browser. Staff awareness can bring forward the small details that automated systems cannot always judge.

The goal is not to treat every unusual sign-in as a breach. Employees travel, work from home, replace phones and occasionally need urgent access outside normal hours. The goal is to identify combinations of signals that deserve attention.

Signals worth investigating

The following events do not always prove an account has been taken over, but they should be reviewed in context:

  • Sign-ins from an unusual country, network or device, particularly where the user is not travelling.
  • Multiple failed sign-in attempts followed by a successful login, or repeated multi-factor authentication prompts.
  • New inbox forwarding rules, deleted messages, changes to recovery details or unfamiliar delegated mailbox access.
  • Unexpected changes to payment information, supplier bank details or approval workflows.
  • Large downloads from cloud storage, unusual file sharing or attempts to access systems outside the employee’s normal role.

For example, a solicitor signing in from a hotel during a planned trip may be entirely legitimate. The same sign-in, followed by a new forwarding rule and a request to amend a client bank account, requires immediate action. Context is what turns an alert into a useful security decision.

Why email accounts are a prime target

Business email compromise is often the commercial outcome of an account takeover. Once inside a genuine mailbox, a criminal can study writing style, invoices, customer relationships and internal approval processes. They may reply to an existing conversation, making a fraudulent request look much more credible than a generic phishing email.

Microsoft 365 is particularly valuable because it brings email, files, Teams conversations and identity together. That is useful for productivity, but it means a compromised account can give an attacker a broad view of the business. Organisations should therefore monitor more than failed password attempts. Mailbox rules, external forwarding, application permissions, file downloads and sign-in patterns all matter.

This is also why a last-minute request to change bank details should never be approved on email alone, even if it comes from a known contact. A simple verification call using an established number can stop a significant loss.

Build detection around the way your business operates

The right level of account takeover detection depends on your risk, the systems you use and how much internal capacity you have. A professional services firm handling confidential client data may need tighter conditional access and detailed audit trails. A logistics business with shift workers, warehouse devices and external partners may need carefully tuned policies so legitimate access is not constantly interrupted.

Start by identifying the accounts that would cause the greatest damage if compromised. This usually includes directors, finance staff, Microsoft 365 administrators, payroll users, people with access to customer data and anyone who can approve payments. These accounts should have strong multi-factor authentication, restricted administrative privileges and closer monitoring.

Next, establish what normal looks like. Which countries do staff work from? Which devices are managed? Who needs access outside business hours? Which third-party applications have access to Microsoft 365 data? Clear answers make alerts more meaningful and reduce unnecessary disruption.

It is tempting to enable every available alert, but that can create alert fatigue. If a small internal team receives dozens of low-value notifications, the important one may be missed. A managed service can be a better fit where there is no dedicated security function, provided responsibilities are clear: who monitors alerts, who contacts staff, and who has authority to disable an account?

The controls that make detection effective

Detection works best alongside preventative controls. Multi-factor authentication remains essential, but it should be set up thoughtfully. Number matching, authentication apps and phishing-resistant methods can reduce the risk of accidental approvals. Where possible, block older sign-in methods that do not support modern authentication.

Conditional access policies can restrict sign-ins based on risk, location, device health and user role. A managed laptop meeting your security standards should be treated differently from an unknown device. That said, policies must be tested against real working patterns, especially for remote teams and staff who need access while travelling.

Endpoint protection is equally relevant. If malware on a device steals browser sessions or passwords, identity controls alone may not be enough. Keeping devices patched, protected and centrally managed gives your business a stronger chance of detecting the cause as well as the suspicious sign-in.

Finally, train people for the decisions they actually make. Staff do not need a technical lecture on identity architecture. They need to know how to report unexpected sign-in prompts, recognise a fake login page, question urgent payment changes and ask for help without embarrassment. Fast reporting is a practical security control.

What to do when an account is compromised

Speed matters, but so does preserving enough evidence to understand what happened. First, disable or block access to the affected account and revoke active sessions. Reset credentials, review multi-factor authentication methods and remove any unfamiliar recovery information. If the account has administrative privileges, check related privileged accounts without delay.

Then investigate what changed. Review sign-in logs, mailbox rules, delegated access, application permissions, file-sharing activity and sent items. Look for other users who may have received the same phishing message or approved suspicious prompts. If payment fraud is possible, contact the bank and affected supplier or customer through a verified channel immediately.

Communication should be calm and practical. Employees need clear instructions, not blame. Depending on the data involved, your business may also need to assess contractual, regulatory and data protection reporting obligations. Keeping an incident record helps demonstrate that the situation was handled responsibly.

Make responsibility clear before an alert arrives

The difficult part of account takeover detection is rarely finding a security setting. It is deciding who owns the response at 7.30am on a busy Monday, when a director cannot access email or finance has spotted a questionable invoice.

Document a short response process, test it and make sure staff know how to reach a real person. For businesses that want expert administration without building an internal security team, MSnet can help bring monitoring, protective controls and staff education into a manageable service. The right arrangement should reduce pressure on your people, not create another complex system for them to run.

A suspicious login may turn out to be a staff member on a train using a new phone. Or it may be the first opportunity to stop a serious incident. Treating both possibilities with prompt, informed attention is how a business protects its people, customers and ability to keep working.

Categories
Cyber Security

Outsourced IT Support Benefits for UK SMEs

A failed laptop at 8.30am, a suspicious Microsoft 365 sign-in, or a member of staff unable to access a key system can quickly become a leadership problem. For many small and medium-sized businesses, the outsourced IT support benefits are not about handing technology to someone else. They are about having a capable, accountable team ready to keep work moving, reduce cyber risk and take pressure off the people running the business.

That matters when internal resources are stretched. A managing director should not have to decide whether an email is a phishing attempt, chase an intermittent Wi-Fi issue, or work out whether company files are genuinely recoverable after an incident. Good outsourced support gives the business a clear route to help, alongside the technical controls and advice needed to prevent avoidable disruption.

Why outsourced IT support benefits extend beyond the helpdesk

The most obvious benefit is access to expertise without the cost and management overhead of building a full in-house IT department. But the real value is broader: a well-run service connects day-to-day support with cyber security, backup, staff training and planning.

A supplier that only fixes faults after they occur may keep users productive in the short term, but it will not necessarily improve the organisation’s resilience. A more useful partner looks for recurring problems, checks whether systems are protected and helps make sensible decisions before a small weakness becomes costly downtime.

For a professional practice, that might mean improving how sensitive client documents are shared and protected. For a logistics firm, it could mean keeping remote users, handheld devices and operational systems available across a busy working day. The right approach depends on the business, but the objective is the same: technology should support operations rather than create another source of uncertainty.

Faster access to people who can help

When an employee cannot work, an automated ticket acknowledgement is not a solution. Small businesses often value direct access to real people who understand their setup and can explain the fix in plain English.

Outsourced support gives users a defined place to go for common issues such as password access, new starter setup, printer faults, Microsoft 365 permissions and device problems. It also gives leaders an escalation route when a problem affects customers, deadlines or essential services.

Speed is important, but context matters too. A provider that knows which systems are business-critical can prioritise appropriately. If a practice management platform or shared file system is unavailable, the response should reflect the operational impact, not simply the order in which tickets arrived.

Better security without asking staff to become specialists

Cyber criminals do not only target large enterprises. Smaller organisations are regularly targeted because a single compromised email account, reused password or unpatched device can provide a straightforward route to valuable information and payment fraud.

An outsourced IT provider can put practical layers of protection around the business, including endpoint security, email filtering, safer internet browsing, credential management and monitoring for exposed details on the dark web. Just as importantly, it can help maintain those measures over time. Security tools that are installed but poorly configured, ignored or left unmanaged can create a false sense of safety.

Technology alone is not enough. Phishing emails are designed to persuade busy people to act quickly, while business email compromise often relies on convincing requests that appear to come from a director, supplier or colleague. Clear, relevant awareness training helps staff recognise the warning signs and know what to do next. That protects the organisation while avoiding blame when people ask for help.

More predictable costs and clearer accountability

Recruiting an experienced IT professional is expensive, and one person cannot reasonably cover every discipline. Support, cloud administration, cyber security, backup, purchasing, user training and strategic planning all require different skills. Annual leave, illness and staff turnover can also leave a small internal team exposed.

With managed support, costs are typically easier to plan. The business can agree a service level and scope that fits its needs, rather than reacting to every issue through ad-hoc call-outs. This does not mean every cost disappears. Hardware replacement, major projects, licences and specialist work may sit outside an ongoing agreement. A credible provider will make that distinction clear from the start.

There is also a useful line of accountability. Instead of different staff members trying to resolve problems with several software vendors, a support partner can take ownership of diagnosis and coordination. That saves time, particularly when an issue crosses devices, internet connectivity, Microsoft 365 and security controls.

Outsourced IT support benefits for continuity and compliance

Downtime is rarely just an IT inconvenience. It can delay client work, interrupt invoicing, prevent teams from communicating and damage confidence in the business. The financial impact is not always visible on a balance sheet immediately, but it is felt in missed deadlines, frustrated staff and management time diverted from core work.

A strong outsourced service supports continuity by making sure the fundamentals are in place: devices are managed, key systems are monitored, access is controlled and data is backed up. It should also test whether recovery is realistic. A backup is only valuable if the business can restore the right data within an acceptable timeframe.

For organisations handling regulated or sensitive information, this approach also supports wider governance responsibilities. Outsourced support cannot remove a director’s responsibility for data protection or risk management, but it can provide evidence, advice and practical controls that make those responsibilities more manageable. This may include reviewing user access, applying security updates, protecting Microsoft 365 data and documenting sensible processes around devices and accounts.

The question is not whether every organisation needs the same compliance framework. It is whether the level of protection matches the data held, the contractual commitments made and the consequences of an incident. A healthcare-adjacent provider, legal firm or financial services business may require more formal controls than a small local operation, but both need to understand their risks.

Support that grows with the business

Technology needs change as businesses recruit, introduce new systems, open locations or support more remote working. An outsourced provider can help with everyday changes such as onboarding staff and provisioning devices, while also offering project expertise when the business needs to move systems, improve security or resolve a complex problem.

This flexible model is particularly useful for growing firms. They may not need a full-time IT manager yet, but they do need informed advice before committing to new software, cloud services or hardware. Decisions made under pressure can create unnecessary cost and complexity for years afterwards.

At MSnet, this can mean choosing the level of help that makes sense: self-service tools for capable internal teams, managed services for businesses that want expert administration, or professional services for defined projects. The important point is that support should fit the business rather than forcing the business into a one-size-fits-all package.

What to check before outsourcing IT support

Outsourcing works best when responsibilities are agreed clearly. Before appointing a provider, establish which users, devices, locations and systems are included, how urgent issues are handled, and what happens outside normal working hours. Ask how the provider manages Microsoft 365, backup, cyber security alerts and staff departures, as these are common points of weakness.

It is also worth asking who will actually provide support. Some providers rely heavily on portals and remote processes, which can suit technically confident organisations. Others offer more direct human contact. Neither model is automatically better, but it should suit the way your staff work and the level of reassurance your leadership team needs.

Avoid choosing on monthly price alone. A cheaper agreement can prove costly if it excludes the systems that matter, provides little proactive work or leaves security as an optional extra. Equally, do not pay for an extensive service model if your internal team is capable of managing much of the day-to-day work. The best arrangement is proportionate, transparent and regularly reviewed.

Good outsourced IT support gives business leaders one less thing to worry about, not another supplier to chase. When people can get help quickly, systems are protected and recovery plans are credible, technology becomes a steadier foundation for the work that matters most.

Categories
Cyber Security

DMARC Implementation Guide for UK Businesses

A convincing fake email from your own domain can do more damage than a blocked spam message ever will. This DMARC implementation guide explains how to stop criminals impersonating your business while protecting legitimate email that keeps your operations moving.

For UK SMEs, email is often where trust is won or lost. A fraudulent invoice, altered bank detail request or fake message from a director can trigger financial loss, data exposure and difficult conversations with customers. DMARC gives your organisation a practical way to tell receiving mail systems which messages are genuinely authorised to use your domain.

What DMARC does for your business

DMARC stands for Domain-based Message Authentication, Reporting and Conformance. It works alongside two existing email controls: SPF and DKIM. SPF identifies the services allowed to send email for your domain. DKIM adds a signed digital marker to emails, allowing receiving systems to verify that a message has not been changed in transit.

DMARC brings these controls together. It checks whether SPF or DKIM passes and, crucially, whether the domain being checked aligns with the visible address your recipient sees in the From field. That alignment is what makes DMARC effective against direct domain impersonation.

You then publish a policy in your domain’s DNS records. The policy instructs receiving email providers what to do when a message fails DMARC checks. You can begin by monitoring failures, move to sending suspicious messages to quarantine, and eventually reject them altogether.

The business benefit is straightforward: fewer opportunities for criminals to trade on your name. It can also improve the likelihood of legitimate email reaching recipients, especially when major providers apply stronger authentication expectations to business senders.

Before you publish a DMARC record

The technical change itself is small. The investigation before enforcement is where most of the work sits. Many businesses send email from more places than they realise, particularly after years of adding cloud tools, marketing platforms and specialist systems.

Start by agreeing who owns the project. This should include whoever manages your domain DNS, Microsoft 365 or other email platform, and the teams responsible for customer communications. Finance, marketing, HR and operations may each use services that send as your domain without involving IT on a day-to-day basis.

Create an inventory of every legitimate sender. Common examples include:

  • Microsoft 365 mailboxes and shared mailboxes
  • CRM, marketing and newsletter platforms
  • Finance, payroll and HR systems
  • Website forms, booking tools and ecommerce platforms
  • Helpdesk, monitoring and document-signing services

Do not rely solely on what staff remember. Review DNS records, procurement records, application settings and email headers from recent messages. Ask suppliers whether their service supports custom DKIM signing and what SPF entries it requires. A platform that sends email on your behalf but cannot authenticate correctly may need configuration changes before your policy becomes stricter.

This discovery stage matters because a reject policy can prevent real messages from being delivered if a legitimate service has been missed. That is not an argument for delaying DMARC indefinitely. It is a reason to implement it in controlled stages.

Set up SPF and DKIM first

DMARC is not a replacement for SPF and DKIM. Both need attention, although DMARC only requires one of them to pass with aligned domains. In practice, configuring both gives you more reliable protection and fewer delivery problems.

Your SPF record is a DNS text record listing authorised sending infrastructure. Keep it accurate and avoid adding providers simply because a setup guide tells you to. Every included service expands the group allowed to send as your domain. SPF also has a limit of ten DNS lookups, so an overgrown record can fail even when it appears correct.

DKIM is generally the more dependable long-term control because it validates a signed message rather than relying on the sending server’s IP address. Enable DKIM for Microsoft 365 and for third-party services wherever possible. Check that the signing domain aligns with the address used in the visible From field. A passing signature from an unrelated supplier domain may not satisfy DMARC alignment.

If you use several related domains, decide which are actively used for email and which should never send it. A parked or defensive domain is still valuable to criminals. It should normally have a restrictive DMARC policy rather than being left unprotected.

DMARC implementation guide: start in monitoring mode

Your first DMARC record should normally use the policy `p=none`. This does not ask receiving systems to block mail. It asks them to send reports so you can see who is using your domain and whether messages pass authentication.

A basic record is published at `_dmarc.yourdomain.co.uk` as a DNS TXT record. It includes a version, a policy and an address for aggregate reports. Those reports are XML files, which are useful but not particularly friendly to read without a reporting service or technical support.

Allow enough time to gather meaningful data. Two to four weeks is often sensible, but the right period depends on your business cycle. A logistics firm may need to see communications across busy operational periods. A professional practice may need to include month-end invoicing, recruitment activity or client campaigns. The goal is to find irregular but legitimate senders before enforcement begins.

During this period, review three things: authorised sources that are failing, unknown sources attempting to use the domain, and whether failures are caused by SPF, DKIM or alignment. Correct the genuine sources first. Unknown sources may be phishing, but investigate before making assumptions, especially where suppliers or regional teams operate independently.

Move from visibility to protection

Once legitimate services consistently pass DMARC, increase the policy to `p=quarantine`. This asks receiving providers to treat failed messages with caution, often placing them in spam or junk folders. It is a useful intermediate stage because it reduces exposure while allowing you to spot any unexpected impact.

Some organisations apply quarantine gradually using the `pct` tag, which applies the policy to a percentage of failing mail. This can be helpful where email flows are complicated, but it should not become a permanent comfort blanket. A low percentage leaves much of your domain available for abuse.

When reporting shows that valid email is correctly authenticated, move to `p=reject`. Receiving systems are then asked to reject messages that claim to come from your domain but fail DMARC. This is the point at which the strongest protection against direct spoofing is achieved.

Keep monitoring after enforcement. New software, mergers, website changes and supplier replacements can all introduce unauthenticated email. DMARC is a business control that needs ongoing ownership, not a one-off DNS task.

Common problems that delay enforcement

The most common issue is treating DMARC as an IT-only exercise. A marketing team may launch a campaign tool, or finance may adopt an invoicing platform, without realising it sends mail as the corporate domain. Clear approval processes help prevent this recurring problem.

Forwarded email can also complicate SPF, because forwarding changes the route a message takes. DKIM often survives forwarding better, which is another reason to configure it carefully. Mailing lists can create similar behaviour. Test real messages rather than relying only on a supplier’s documentation.

Subdomains require attention too. Your main DMARC policy can apply to them by default, but some organisations use subdomains for marketing, support or transactional email and need separate policies. Make this an intentional decision. A forgotten subdomain can become an easy impersonation route.

Finally, DMARC cannot stop every form of email fraud. Attackers can use lookalike domains, compromised accounts or convincing social engineering. It works best alongside multi-factor authentication, email filtering, secure backup, and staff awareness training that gives people confidence to question unusual requests.

Decide how your organisation will manage DMARC

Technically confident organisations may manage the records and reports themselves, provided there is a named owner and a process for reviewing changes. Others will prefer a managed service, particularly where Microsoft 365, multiple suppliers and limited internal IT time make reporting harder to interpret.

The right approach depends on your email estate and risk profile. A small business with one Microsoft 365 tenant may need focused setup and periodic checking. A regulated firm, multi-site operation or company handling sensitive financial requests may benefit from continuous monitoring and expert support. MSnet can help businesses assess their email estate, configure authentication correctly and keep the protection working as systems change.

A properly enforced DMARC policy is one less thing for your team to worry about when criminals try to impersonate your business. Start with a clear picture of what sends email for you, make legitimate services accountable, and let every policy change be guided by evidence rather than guesswork.

Categories
Cyber Security

Cybersecurity Consultancy That Reduces Risk

A suspicious Microsoft 365 sign-in, a supplier’s altered bank details or one employee entering credentials on a convincing fake page can create a serious business problem within minutes. For a small or medium-sized business, the impact is rarely limited to IT. It can interrupt operations, expose confidential information, delay customer work and leave directors answering difficult questions.

Cybersecurity consultancy gives leaders a clear, practical route through that risk. Rather than asking your team to become security specialists, it identifies where the business is exposed, prioritises the actions that will make a genuine difference and helps put the right protections in place.

What cybersecurity consultancy should achieve

Good consultancy is not a report full of technical language that sits unread after a meeting. It should help your organisation make better decisions about risk, investment and responsibility.

For most UK SMEs, that starts with understanding the essentials: who can access which systems, where business data is held, how devices are protected, whether backups can be restored and how staff respond to suspicious emails. It also means considering the risks created by remote working, third-party suppliers, personal devices and cloud services.

The aim is proportionate security. A professional services firm handling sensitive client records has different priorities from a logistics company that depends on continuous access to operational systems. Both need protection, but the controls, recovery requirements and staff training should reflect how they work.

Effective advice should therefore reduce uncertainty. You should come away knowing what needs attention now, what can be planned for later and why each action matters commercially.

When your business may need cybersecurity consultancy

Many businesses seek advice after a phishing incident, ransomware scare or failed compliance review. Those are valid triggers, but waiting for a problem can be costly. Consultancy is often most valuable when the business is changing or when existing IT arrangements no longer provide enough confidence.

You may need support if you are moving to Microsoft 365, expanding remote working, opening a new site, changing IT suppliers or introducing systems that hold more customer data. It is also sensible to seek an independent view if nobody can clearly explain your current backup arrangements, recovery times or the protections applied to company laptops and mobile devices.

Other warning signs are less technical. Perhaps staff regularly forward files to personal email accounts to get work done, former employees’ accounts are not always removed promptly, or directors receive payment requests without a reliable verification process. These are operational weaknesses as much as technology issues.

A consultant should be able to translate those concerns into a manageable plan, without making every risk sound like a catastrophe. No organisation can remove all risk. The sensible goal is to prevent the most likely and damaging incidents, spot trouble early and recover quickly if something does get through.

A practical cybersecurity consultancy process

The best engagements begin with questions about the business, not a product list. What would happen if email stopped working for two days? Which information would cause the greatest harm if it was disclosed? Are there contractual, regulatory or insurance requirements to meet? Who needs rapid access to systems during an incident?

Assess the real attack surface

A useful assessment examines the systems people rely on every day. This usually includes Microsoft 365 accounts, endpoints, servers, cloud storage, email settings, internet browsing controls, backups, administrator access and third-party connections.

It should also look for common gaps such as weak or reused passwords, missing multi-factor authentication, unpatched software, excessive user permissions and devices that are not properly managed. Dark web monitoring can help identify exposed credentials, but it is only useful when there is a clear process for responding to alerts.

The result should be understandable to leadership. A risk register is helpful, but so is a straightforward explanation of the likely business impact, the recommended action, the owner and the expected cost or effort.

Prioritise the actions that matter

Not every finding deserves the same response. A critical vulnerability on an internet-facing system needs prompt action. An improvement to a low-risk internal process may be scheduled as part of a wider IT plan.

For many SMEs, the first priorities are identity protection, endpoint security, email protection and recoverable backups. These areas address a large proportion of everyday threats, including phishing, business email compromise, credential theft and ransomware.

A consultancy engagement should avoid recommending security tools simply because they are available. The right choice depends on your existing technology, internal skills, budget and appetite for ongoing management. Buying a sophisticated platform without the capacity to monitor and maintain it can create false confidence.

Put controls into everyday operations

Security only works when it fits how people work. Multi-factor authentication, for example, is highly effective but should be introduced with clear communication and sensible recovery arrangements. Staff need to know what to do if they change phones, lose a device or receive an unexpected approval prompt.

The same applies to backup. A backup service is not the same as a recovery plan. Your business should know what is backed up, how often, where copies are held, who can restore them and how long a realistic restoration will take. Testing matters because recovery is often most difficult when the pressure is already on.

Where internal IT resources are limited, managed services can take the ongoing administration off your team’s plate. Technically capable organisations may prefer self-service tools and expert advice when needed. Project-based professional services can suit a specific migration, security review or remediation programme. The right model depends on how much responsibility you want to retain.

People remain part of the security control

Cybercriminals often choose the easiest route into a business: a busy person. A well-crafted phishing email can look like a message from a director, supplier, bank or Microsoft. It may not contain obvious spelling mistakes, and it may arrive at exactly the moment an employee is expecting an invoice or password reset.

That is why staff awareness should be practical, regular and free from blame. People need to recognise warning signs, but they also need permission to pause and ask for help. A culture that values reporting can stop a minor mistake becoming a major incident.

Training is most effective when it reflects real roles. Finance teams should understand payment diversion fraud and verification procedures. Reception and operations staff may need guidance on social engineering calls. Remote workers should know how to protect devices, home networks and sensitive conversations. Directors need to understand their own heightened exposure to impersonation and account takeover.

Technical controls and education work together. Email filtering can block many malicious messages, while staff training provides a second line of defence when an unusual message reaches an inbox. Credential management can reduce password risk, while multi-factor authentication limits the damage if a password is stolen.

Compliance should support better security

For regulated organisations and businesses handling personal or commercially sensitive information, cybersecurity has a compliance dimension. Clients, insurers and regulators increasingly expect evidence that risks are understood and managed.

However, compliance checklists should not become the whole strategy. A policy that nobody follows will not protect customer data or keep operations running. The strongest approach uses governance to support practical controls: documented access processes, tested backups, incident response responsibilities, staff training records and regular reviews of suppliers.

Cyber Essentials can provide a useful baseline for many UK businesses, particularly where tenders or customer requirements make certification relevant. It is not a guarantee against attack, but the disciplines behind it can address common weaknesses. Whether certification is appropriate depends on your market, contracts and current security maturity.

Questions to ask before choosing a consultant

The quality of advice matters as much as the technology being recommended. Ask whether the consultant has experience with organisations of your size and sector, and whether they can explain risks in plain English to non-technical decision-makers.

You should also understand what happens after the assessment. Will you receive an actionable plan? Can the provider help implement the recommendations, train staff and support you when an incident occurs? Is there direct access to knowledgeable people, or will urgent questions disappear into a ticket queue?

Be wary of a one-size-fits-all proposal that arrives before anyone has taken the time to understand your business. A dependable partner will be honest about trade-offs, including where a lower-cost option is adequate and where investment is needed to protect a critical service.

For businesses that want clear advice alongside hands-on protection, MSnet can combine consultancy with managed controls, targeted training and real human support. The purpose is not to add another complex technology project. It is to give your business a more confident, workable position against cyber risk.

The most useful next step is often a conversation about what keeps you awake at night: a loss of email, inaccessible files, a fraudulent payment or uncertainty over whether your backups would work. Start there, and build protection around the way your organisation actually operates.

Categories
Cyber Security

How to Manage Microsoft 365 Without Added Risk

A former employee’s inbox is still active. A shared folder has been opened to anyone with the link. A director receives an apparently genuine payment request. These are ordinary situations, but they show why knowing how to manage Microsoft 365 is about much more than creating accounts and renewing licences.

For a small or medium-sized business, Microsoft 365 is often where email, documents, meetings, customer information and day-to-day decisions live. It needs to be managed as a core business system: securely, consistently and with enough oversight that problems are spotted before they disrupt the working day.

Start with ownership and a clear administration model

The first question is not which setting to switch on. It is who is accountable for Microsoft 365. In many businesses, administration gradually falls to the person who knows a little more about technology than everyone else. That can work for a while, but it creates risk when access, security alerts and user changes rely on one busy individual.

Give named people responsibility for the tenant, with at least two trusted administrators to avoid a single point of failure. Keep a secure record of the tenant details, domain renewal information, emergency contacts and the processes used to approve new accounts or access changes. These are practical continuity measures, particularly if a key member of staff is unavailable.

Not every administrator needs the same level of power. Use role-based access instead of making several people Global Administrators. A finance lead may need visibility of billing. A service manager may need to reset passwords or manage Teams. Full control should be restricted to a very small number of trusted people and used only when necessary.

Manage identities before they become an incident

Most Microsoft 365 breaches begin with a compromised identity, not a dramatic technical failure. A criminal only needs one password, one successful phishing email or one poorly protected account to gain a foothold.

Multi-factor authentication should therefore be standard for every user, including directors and administrators. Where possible, use an authenticator app or security key rather than relying solely on text messages. Passwords still matter, but a strong password alone is no longer sufficient protection for business email.

Conditional access can add another useful layer by checking the context of a sign-in. For example, a business may require stronger verification when someone signs in from an unfamiliar country, blocks legacy authentication, or prevents access from devices that do not meet the required security standard. The right policy depends on how and where people work. A professional practice with staff largely based in the UK may take a different approach from a logistics business with teams travelling internationally.

Joiners, movers and leavers need a routine that is followed every time. New starters should receive only the access they need. When someone changes role, review the groups, shared mailboxes and files they can reach. When they leave, block sign-in promptly, preserve business information where required, transfer ownership of key documents and remove licences at the appropriate point. Delaying this work leaves dormant accounts that are easy to overlook and attractive to attackers.

Set a sensible security baseline for email and files

Email remains a preferred route for phishing, invoice fraud and malware. Microsoft 365 includes valuable security controls, but they need to be configured, monitored and reviewed. Anti-phishing policies, spam filtering and attachment protection can reduce exposure, while impersonation protection helps identify messages pretending to come from a director, supplier or trusted customer.

Technology cannot decide whether a payment request is genuine or whether a colleague has been tricked into approving access. Staff need clear, short guidance on what to look for and what to do next. Regular phishing awareness training works best when it reflects real situations: changed bank details, urgent document-sharing requests, missed-delivery messages and fake Microsoft sign-in pages. The objective is not to catch people out. It is to make reporting suspicious activity a normal and easy part of the working day.

File sharing also deserves close attention. SharePoint and OneDrive make collaboration far easier, but unrestricted external sharing can expose confidential material. Decide which teams may share externally, whether guests require approval, how long links should remain active and whether sensitive folders should be excluded altogether.

Sensitivity labels and data loss prevention policies can help where you handle personal, financial, legal or commercially sensitive information. They are particularly useful in regulated organisations, but they must be introduced carefully. Overly restrictive rules can stop legitimate work and encourage staff to find less secure workarounds. Start with the highest-risk data and refine policies based on how people actually work.

Keep devices under control

A secure Microsoft 365 account accessed from an unmanaged, poorly patched laptop is still a concern. Device management connects user security to the equipment people use every day.

Use a managed device platform to enforce essentials such as screen locks, encryption, supported operating system versions and security updates. It should also allow business data to be removed from a lost or stolen device without affecting an employee’s personal files where a bring-your-own-device policy is permitted.

This is an area where proportion matters. A business supplying corporate laptops to every employee can set firmer controls than one with occasional contractors using their own devices. Either way, define what is acceptable before a problem occurs. Remote working should not mean unknown devices have unrestricted access to company information.

Review licences, permissions and configuration regularly

Microsoft 365 costs can quietly increase as people join, roles change and projects end. A quarterly review of active users, licences and add-ons keeps spending aligned with real needs. It can also reveal accounts that should have been removed or shared mailboxes that have become unmanaged repositories for sensitive information.

Permissions deserve the same attention. Teams and SharePoint sites often outlive the projects that created them. Owners move on, guest users remain, and folders become difficult to govern. Assign accountable owners to important sites and groups, then review membership and external access on a planned basis.

Configuration reviews should cover more than licences. Check that multi-factor authentication is still enforced, audit logs are available, administrator roles remain appropriate, email policies are working as expected and alerts are reaching someone who will act on them. Security settings are not a one-off project. Microsoft changes its services, threats change, and your business changes too.

Back up Microsoft 365 separately

Microsoft 365 provides resilience and retention features, but that is not the same as having a complete, independent backup strategy. Deleted files, accidental overwrites, malicious encryption and retention gaps can all create recovery problems. The ability to retrieve an individual email, a SharePoint folder or a former employee’s OneDrive data can save considerable time and stress.

A proper backup should cover the services your business relies on, commonly Exchange Online, OneDrive, SharePoint and Teams data. Just as importantly, test restoration. A backup that has never been checked is a promise rather than a recovery plan.

Agree who can request a restore, who approves it and how quickly different types of data need to be recovered. For a client-facing professional services firm, an urgent mailbox recovery may be business-critical. For archived project material, a slower recovery may be acceptable. These priorities help you invest sensibly rather than paying for controls that do not match the risk.

Make monitoring and response part of normal operations

Even well-configured systems need watching. Suspicious sign-ins, unexpected mailbox rules, large file downloads and changes to administrator permissions can all indicate a problem. The challenge for smaller organisations is that alerts often arrive without anyone having the time or confidence to investigate them.

Create a simple response process for Microsoft 365 incidents. Staff should know where to report a suspected phishing email. Managers should know who to contact if a device is lost. Administrators should know how to disable an account, revoke active sessions and preserve evidence if a compromise is suspected. Speed matters, but so does calm decision-making.

For many businesses, this is where outsourced management is most valuable. A capable internal team may prefer self-service tools and occasional expert advice. Others want a managed service with real people monitoring, maintaining and responding when something does not look right. MSnet can help businesses choose the level of support that fits their in-house capability, compliance needs and budget.

Give Microsoft 365 the attention it deserves

The best approach is not to chase every new feature or security alert. It is to establish clear ownership, protect identities, control data sharing, secure devices, maintain recoverable backups and review the environment regularly. That turns Microsoft 365 from a collection of apps into a dependable platform for the business.

When the right controls and support are in place, leaders spend less time worrying about accounts, suspicious emails and missing files, and more time running the organisation. That is the real measure of well-managed Microsoft 365.